
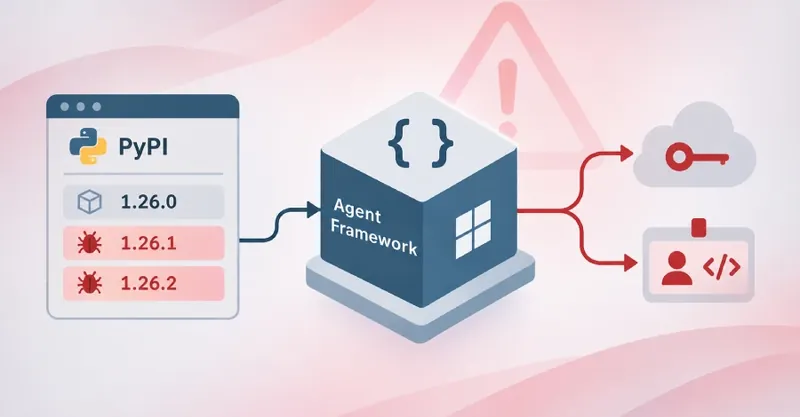
Microsoft’s AI Agent Framework Hit by Malicious PyPI Packages That Steal Cloud Credentials
Original headline: Attackers Compromise Microsoft's Agent Framework PyPI Package to Steal Cloud Credentials — thehackernews.com
More in Cybersecurity news
Threat actors have compromised Microsoft's official 'agent-framework' Python package on the PyPI repository, pushing malicious versions (1.26.1 and 1.26.2) designed to steal cloud credentials. The packages, published on November 17, 2026, install stealthy startup hooks that automatically run a credential stealer on every Python interpreter launch—even if the framework is never imported. The attack leverages .pth files placed in the site-packages directory to execute the payload silently.
The stealer harvests environment variables, credential files (Azure CLI, npm, pip, Git, Docker, Hugging Face), and Azure DevOps/OIDC tokens, and can even request new tokens dynamically—meaning rotating stored secrets may not be enough. Multiple security firms (Aikido, Endor Labs, OX Security, SafeDep, Socket, StepSecurity, Wiz) have confirmed the compromise, and the malicious versions have been quarantined on PyPI. Engineers using Python in cloud or CI/CD environments must immediately check for these versions and assume credentials exposed.
What to do: Check for and remove versions 1.26.1 and 1.26.2 of the agent-framework package from your Python environments.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works