
Optimizely's 'Experimentation' Just Included Card Skimming on CNN and BBC
Original headline: Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors — thehackernews.com
More in Cybersecurity news
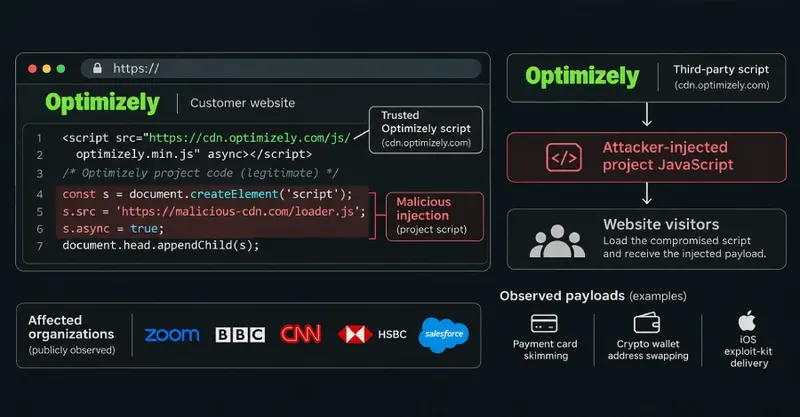
Optimizely's Web Experimentation platform got hijacked by attackers who injected malicious JavaScript directly into customer projects served from its own Content Delivery Network. The compromised scripts, which loaded from Optimizely's own domain with its own certificate, reached visitors of at least 178 major sites including CNN, BBC, and Zoom. The malicious code was designed to steal cryptocurrency by replacing wallet addresses and capture payment card details from unsuspecting users.
The attack wasn't subtle—it exploited a vulnerability that gave the attacker write access to entirely unrelated customer projects. Even after an initial cleanup, Smartsheet's script got re-infected with hidden code, suggesting lingering access. While Optimizely says it fixed the flaw and removed the malicious code, it left critical questions unanswered: how the vulnerability worked, how many projects were changed, and what customers should do now. This is a masterclass in supply chain attack execution—turning a trusted optimization service into a malware delivery system.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works