
Windows is snitching on your IDE to the mothership
Original headline: Coding on Windows? Redmond May Already Know. — hackaday.com
More in Semiconductor and chip news
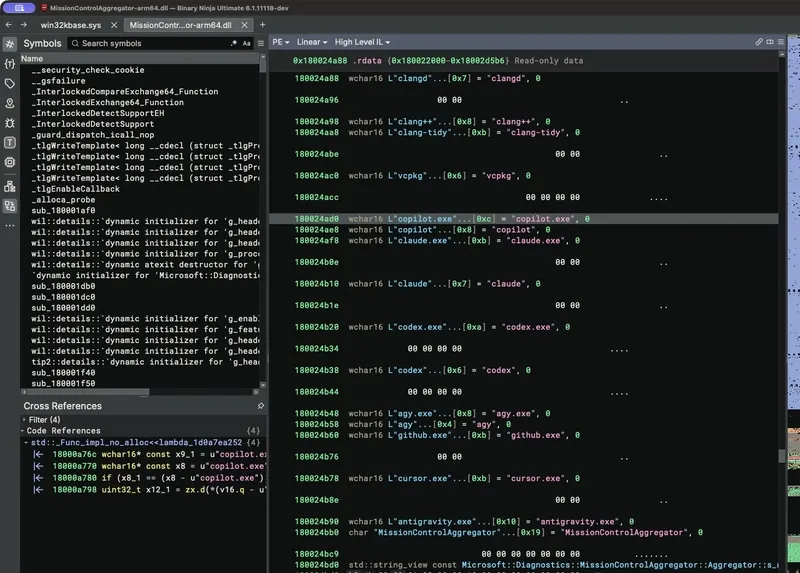
A hacker digging into a recent Windows 11 build discovered a library called MissionControlAggregator.dll that keeps a watchlist of executables on your machine. This list includes common developer tools like Python and GCC compilers, as well as AI agents. While Microsoft could frame this as local system monitoring, the investigation found that launching these listed applications triggers a diagnostic event that, by default on a standard Windows 11 install, promptly sends that information back to Microsoft's servers. Even running these tools within the Windows Subsystem for Linux (WSL) doesn't bypass the surveillance, as the same telemetry event is generated.
The impact is straightforward: millions of developers using Windows for coding are, likely unknowingly, broadcasting their tool usage to Microsoft. This happens under the umbrella of 'optional diagnostics,' which are enabled by default with minimal user awareness during setup. The takeaway is a classic Microsoft move: baking deep, opaque surveillance into the operating system under the guise of helpful diagnostics, leaving users to dig through privacy settings to opt-out—if they even know what to look for.
Read the original at hackaday.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works