
Russian hackers breach U.S. agency using stolen Google Workspace credentials
Original headline: Russian COLD RELIC Hackers Use Stolen Google Workspace Data to Breach Second U.S. Organization — thehackernews.com
More in Cybersecurity news
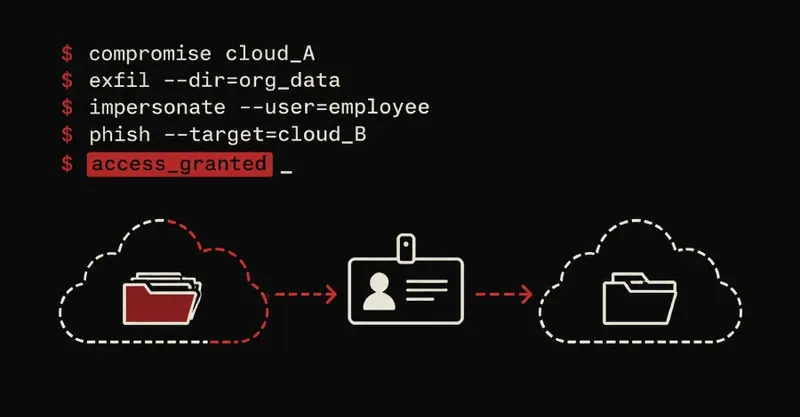
Russian state-backed hackers known as Cold Relic have successfully breached a second U.S. organization by repurposing data stolen from an earlier 2025 Google Workspace compromise. The group, tracked by various names including COLDRIVER and Star Blizzard, used stolen corporate directories and employee identities from their first victim to launch sophisticated phishing attacks against a new target, ultimately gaining Super Admin access through MFA push notification fatigue attacks.
For engineers and security teams managing cloud infrastructure, this attack demonstrates how a single cloud compromise can cascade into third-party breaches through credential reuse and social engineering. The attackers registered their own devices within compromised tenants, used passkeys and MFA backup codes for persistence, and systematically exfiltrated data by mass-sharing files to their own accounts. This incident underscores the critical importance of monitoring privileged cloud access and implementing stricter controls around MFA registration and user directory exposure.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works