
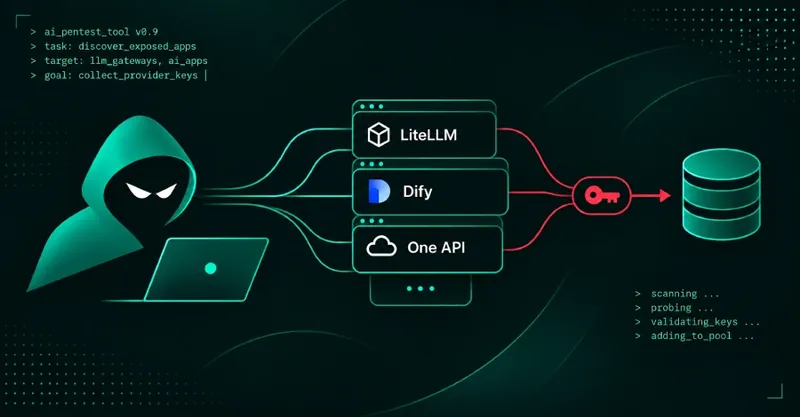
AI hacking agents hunted for weak AI apps to steal their API keys, Amazon found
Original headline: Amazon Uncovers AI Agent Campaign Targeting LiteLLM, Dify, and Other Apps for API Keys — thehackernews.com
More in Cybersecurity news
Amazon's threat intelligence team discovered automated AI hacking agents actively scanning the internet for AI applications like LiteLLM, Dify, and One API. These agents were hunting for known weak spots, such as default admin passwords, unfinished installations, and known vulnerabilities, to steal the API keys stored inside. The agents were powered by an open-source penetration testing tool called ARTEX, which uses large language models to plan and execute tasks. Once stolen, the keys were verified and added to a shared pool, used to power the agents themselves in a self-sustaining cycle.
The real-world impact means any publicly exposed AI app with weak credentials is now a target for automated, AI-driven exploitation. Developers and administrators must urgently secure these endpoints by changing default credentials, applying patches, and removing unfinished installs from public access. This campaign highlights a new frontier in automated cybercrime, where attackers use stolen resources to fuel more attacks, creating a dangerous feedback loop.
What to do: Change default administrator credentials for AI apps like LiteLLM, secure unfinished installs, and apply patches for known flaws in Langflow and RAGFlow.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works