
Qubole supply chain breach: stolen vendor key unlocks customer data
Original headline: Supply chain attack on Qubole customers — sentra.io
More in Cybersecurity news
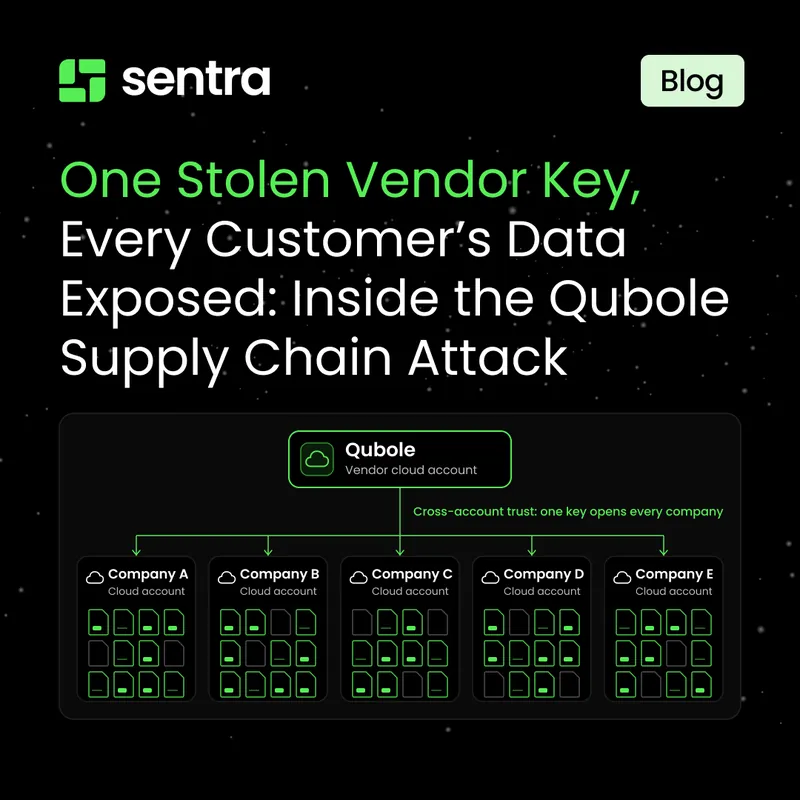
A critical supply chain attack compromised Qubole, a big-data platform, exposing dozens of its enterprise customers. The attacker stole vendor credentials and used Qubole's pre-existing, trusted access to silently pull sensitive data from multiple organizations without directly breaching their systems.
The attack highlights a widespread and dangerous oversight: forgotten cloud integrations with third-party vendors create 'doors' that remain trusted, unwatched, and capable of reaching sensitive data. This incident serves as a stark reminder that your security perimeter now includes every vendor and automated identity with standing access to your cloud, and that few teams monitor for when these trusted entities start behaving abnormally.
What to do: Audit and revoke all standing access granted to Qubole and similar third-party integrations in your cloud environment.
Read the original at sentra.io
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works