
A Russian ransomware kingpin got doxed by his own mistakes
Original headline: Who Runs the Ransomware Group Qilin? — krebsonsecurity.com
More in Cybersecurity news
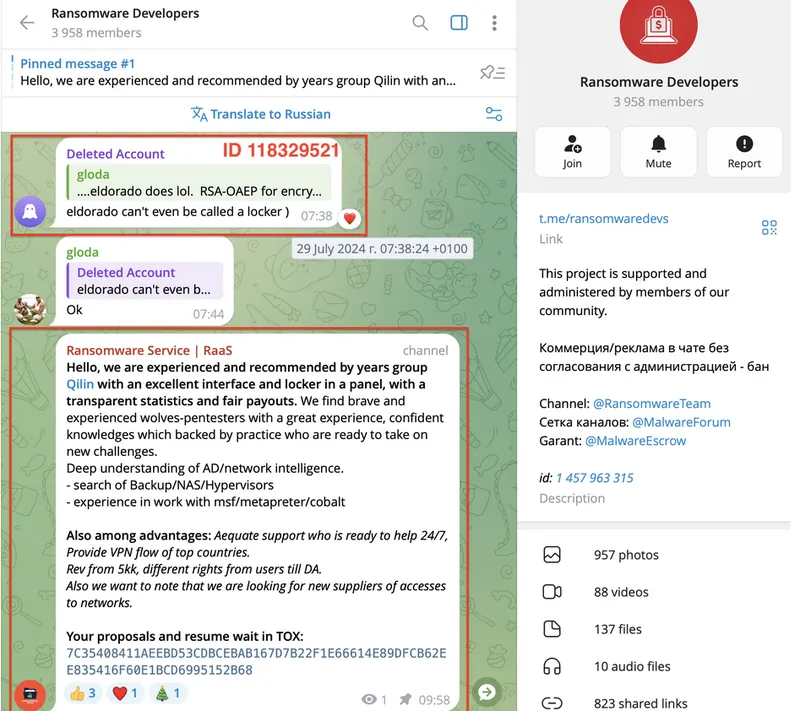
The Qilin ransomware group has become the world's most active digital extortion operation, claiming over 365 victims in just three months. Based in Russia, Qilin operates a 'ransomware-as-a-service' model, paying affiliates up to 80% of ransoms to hack companies and deploy malware using the 'double extortion' technique of stealing data before encrypting systems.
Despite Qilin's industrial-scale criminal success, its administrator—who uses the handle 'Haise'—made critical operational security blunders over the past decade. Investigators traced his identity to a 36-year-old man in St. Petersburg by linking his current alias to older forum accounts, including one discovered in seized FBI data from the RAMP cybercrime forum. This case shows how even the most prolific cybercriminals can be exposed by their own digital footprints.
Read the original at krebsonsecurity.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works