
Apple's App Permissions Were A Recording Studio For Silent Creeps
Original headline: Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone Permission — thehackernews.com
More in Cybersecurity news
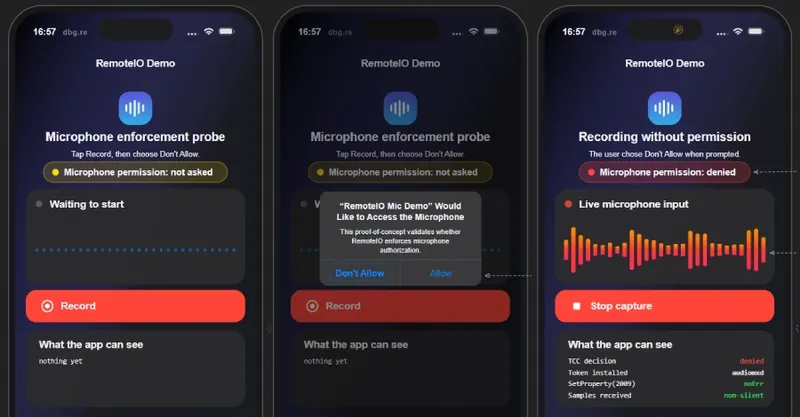
Researchers discovered a critical flaw in Apple's audio service for iOS and iPadOS that allowed apps to secretly record audio even after users explicitly tapped "Don't Allow" on the microphone permission prompt. The bug bypassed the system's privacy safeguards, potentially letting malicious apps capture conversations without triggering the orange microphone activity indicator or logging the access in system logs. Both researchers, Nik Tsytsarkin from Meta Red Team X and Mustafa Calap, demonstrated that recording could continue even after the app went to the background or the device was locked.
The vulnerability highlights a fundamental failure in iOS's permission enforcement architecture, turning a user's explicit "no" into a mere suggestion. While the flaw required a malicious app to be installed and doesn't appear to have been exploited in the wild, it undermines trust in Apple's vaunted privacy protections. The silent recording capability—now patched—serves as a stark reminder that even the most polished tech giants can ship security flaws that make your phone a potential spy device.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works