
A new universal XSS bug let websites hijack uBlock Origin, but it's fixed now
Original headline: Universal XSS in uBlock Origin from website-driven element picker — iter.ca
More in Cybersecurity news
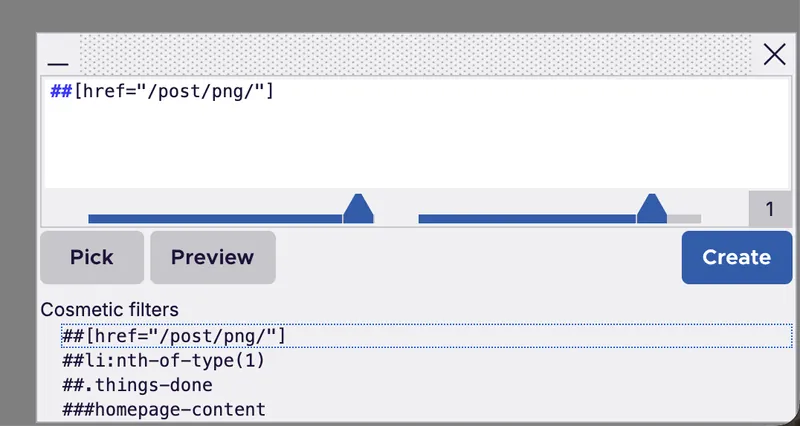
A security researcher, with significant help from AI assistants like GPT-5.6 Sol and Claude, discovered a serious one-click universal cross-site scripting (UXSS) vulnerability in the uBlock Origin browser extension. The flaw was present in the legacy Firefox (MV2) version and a similar, less severe variant affected the newer MV3 version (uBO Lite). This vulnerability allowed a malicious website to trick the extension's element picker tool into adding "trusted" filters, which can inject JavaScript. This would let an attacker run arbitrary code on *any* website visited by the user, potentially stealing data or performing actions on their behalf.
The issue hinged on a website being able to discover the extension's unique internal ID and then programmatically drive an invisible instance of the element picker's iframe. By positioning an invisible "Create" button under the user's cursor, a single click could be hijacked to silently install a malicious, trusted filter. This filter could then execute attacker-controlled JavaScript on subsequent page loads of *any other site*. The vulnerability is now patched, but it serves as a stark reminder of the immense power browser extensions hold and the critical importance of keeping them updated.
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works