
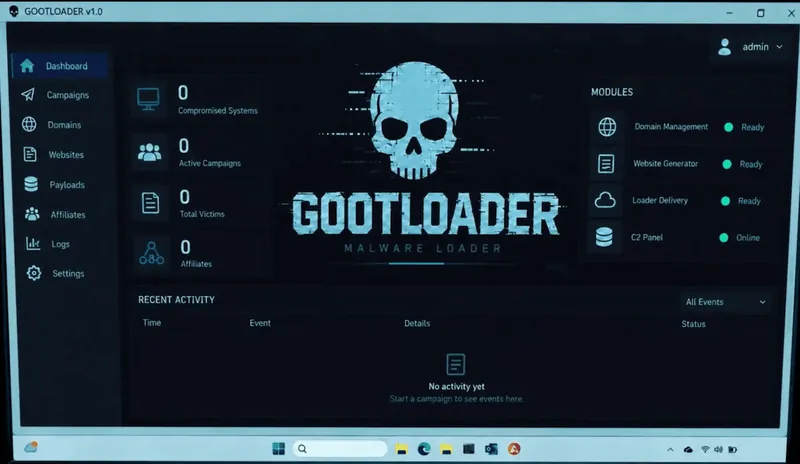
DOJ dismantles Gootloader botnet after 44 ransomware attacks caused $29M in damages
Original headline: DOJ: Gootloader used in at least 44 ransomware attacks costing $29 million since 2018 — therecord.media
More in Cybersecurity news
An international coalition of law enforcement agencies, including the U.S. Justice Department and FBI, dismantled the infrastructure behind Gootloader, a malware strain active since 2018. The operation, part of 'Operation Endgame,' seized over 100 servers and 257 domains used to infect 25,000 devices globally. Victims unknowingly downloaded Gootloader through compromised websites, adding their computers to a botnet that hackers sold access to for ransomware attacks.
The malware was used in at least 44 ransomware attacks on U.S. organizations, resulting in $28.8 million in losses, including targeting the U.S. Department of War and Defense Industrial Base. The takedown involved coordinated technical disruption, victim notifications, and remediation efforts with organizations like the Shadowserver Foundation. This operation demonstrates law enforcement's ongoing efforts to dismantle major cybercriminal infrastructure that fuels the ransomware ecosystem.
Read the original at therecord.media
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works