
Apple's latest iOS update? It's missing the one patch security researchers begged for.
Original headline: Binance Warns of iOS Sandbox Escape That Could Expose Crypto Wallet Keys, No Fix Confirmed — thehackernews.com
More in Cybersecurity news
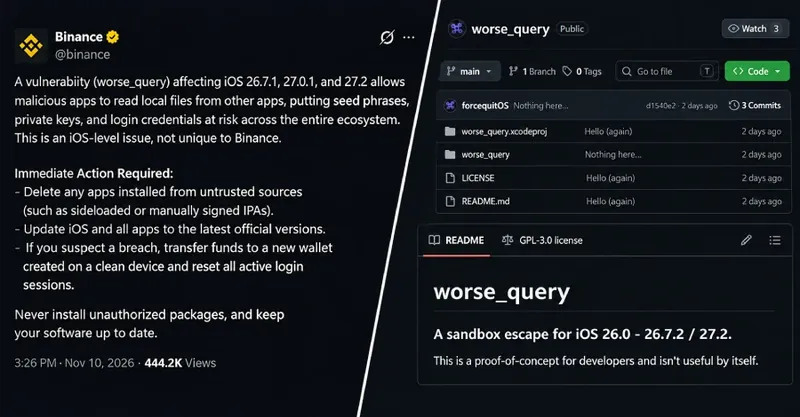
A newly disclosed iOS sandbox escape, dubbed 'worse_query', lets any app with an App Group container read the data containers of other apps on iPhones running iOS 26 and 27. Researchers published proof-of-concept code, which developers have already turned into tools like the WQ Files app manager, allowing access to private keys, seed phrases, and login credentials without a jailbreak. Binance has issued a stark warning about the vulnerability, though Apple's latest iOS updates, released after the disclosure, conspicuously lack any mention of fixing this critical flaw.
The crypto exchange is advising users to delete sideloaded apps, update everything, and—in case of suspected compromise—move funds to a new wallet on a clean device. The core problem is that Apple's security notes make no mention of this sandbox escape, leaving millions of iPhone users potentially exposed through apps that can be installed via unofficial channels like AltStore. The takeaway? When your phone's security relies on Apple patching holes, and they ship an update that ignores the gaping one everyone's talking about, it's time for some serious side-eye at Cupertino.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works