
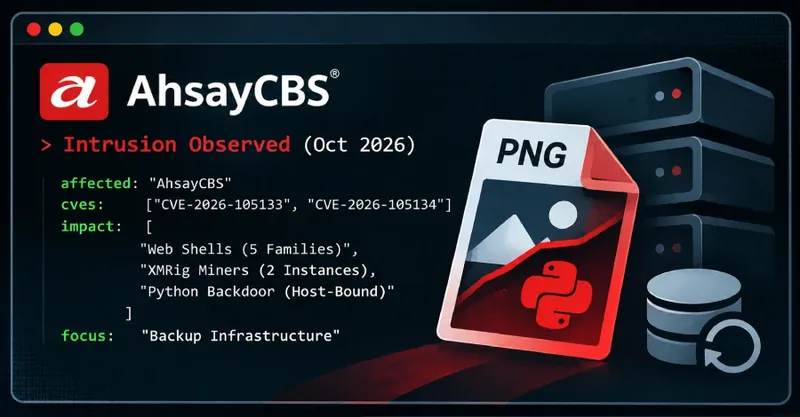
Zero-Day Attack Hits Ahsay Backup Servers, Deploys Elusive Python Backdoor
Original headline: Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor — thehackernews.com
More in Cybersecurity news
A sophisticated attack campaign exploited two previously unknown zero-day vulnerabilities in AhsayCBS backup software to deploy a persistent Python implant alongside cryptocurrency miners and tunneling tools. The flaws, tracked as CVE-2026-105133 and CVE-2026-105134, allowed attackers to bypass authentication and execute arbitrary commands, turning backup servers—critical systems meant to protect data—into beachheads for further intrusion.
The intrusion was notably patient and extensive, with attackers placing multiple types of web shells, including one that hides encrypted code within PNG images, to evade detection. This incident underscores the severe risk when backup infrastructure itself is compromised, as it provides attackers with a trusted position to stage tools, exfiltrate data, and maintain persistence. Organizations using AhsayCBS must immediately verify they have applied the patches released in October 2026.
Read the original at thehackernews.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works